'com.rsa.authmgr.admin.tokenmgt.ListTokensByPrincipalCommand execution' error when trying to assign a token on RSA Authentication Manager 8.x
Originally Published: 2018-09-27
Last Modified: 2022-06-20
Article Number
Applies To
RSA Product/Service Type: Authentication Manager
RSA Version/Condition: 8.x
Issue
=Unexpected error during command com.rsa.authmgr.admin.tokenmgt.ListTokensByPrincipalCommand execution
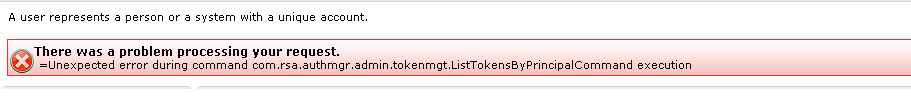
The System Activity Monitor (Reporting > Real Time Activity Monitor > System Activity Monitor or Reporting > Reports > Add New > System Activity) shows the following error:
com.rsa.common.UnexpectedDataStoreException: javax.naming.directory.InvalidSearchFilterException: Missing 'equals';
remaining name 'CN=Ahmed,CN=Users,DC=2k12-vcloud,DC=local',
	at com.rsa.ims.admin.dal.ldap.IdentitySourceAccessLDAP.checkISDN(IdentitySourceAccessLDAP.java:785),
	at com.rsa.ims.admin.dal.ldap.IdentitySourceAccessLDAP.getIdentitySourceWithDN(IdentitySourceAccessLDAP.java:670),
	at com.rsa.ims.admin.dal.ldap.IdentitySourceAccessLDAP.getIdentitySourceWithDN(IdentitySourceAccessLDAP.java:643),
	at com.rsa.ims.admin.impl.IdentitySourceAdministrationImpl.trustedGetIdentitySourceWithDN(IdentitySourceAdministrationImpl.java:2152),
	at sun.reflect.NativeMethodAccessorImpl.invoke0(Native Method),	at sun.reflect.NativeMethodAccessorImpl.invoke(NativeMethodAccessorImpl.java:57),
	at sun.reflect.DelegatingMethodAccessorImpl.invoke(DelegatingMethodAccessorImpl.java:43),
	at java.lang.reflect.Method.invoke(Method.java:606),
	at org.springframework.aop.support.AopUtils.invokeJoinpointUsingReflection(AopUtils.java:317),
	at org.springframework.aop.framework.ReflectiveMethodInvocation.invokeJoinpoint(ReflectiveMethodInvocation.java:183),
	at org.springframework.aop.framework.ReflectiveMethodInvocation.proceed(ReflectiveMethodInvocation.java:150),
	at org.springframework.aop.interceptor.ExposeInvocationInterceptor.invoke(ExposeInvocationInterceptor.java:91),
        at org.springframework.aop.framework.ReflectiveMethodInvocation.proceed(ReflectiveMethodInvocation.java:172),
        at org.springframework.aop.framework.JdkDynamicAopProxy.invoke(JdkDynamicAopProxy.java:204),
        at com.sun.proxy.$Proxy129.trustedGetIdentitySourceWithDN(Unknown Source),
        at com.rsa.ims.admin.impl.PrincipalAdministrationImpl.trustedLookup(PrincipalAdministrationImpl.java:5906),
        at com.rsa.ims.admin.impl.PrincipalAdministrationImpl$4.run(PrincipalAdministrationImpl.java:1936),
	at com.rsa.ims.admin.impl.PrincipalAdministrationImpl$4.run(PrincipalAdministrationImpl.java:1),
	at com.rsa.ims.security.spi.SimpleSecurityContextImpl.doAs(SimpleSecurityContextImpl.java:113),
	at com.rsa.security.SecurityContext.doAs(SecurityContext.java:439),
	at com.rsa.security.SecurityContext.doAsSystem(SecurityContext.java:474),
	at com.rsa.ims.admin.impl.PrincipalAdministrationImpl.lookup(PrincipalAdministrationImpl.java:1933),
	at com.rsa.ims.admin.impl.PrincipalAdministrationImpl.lookup(PrincipalAdministrationImpl.java:1912),
	at sun.reflect.NativeMethodAccessorImpl.invoke0(Native Method),
        at sun.reflect.NativeMethodAccessorImpl.invoke(NativeMethodAccessorImpl.java:57),
        at sun.reflect.DelegatingMethodAccessorImpl.invoke(DelegatingMethodAccessorImpl.java:43),
	at java.lang.reflect.Method.invoke(Method.java:606),
	at org.springframework.aop.support.AopUtils.invokeJoinpointUsingReflection(AopUtils.java:317),
	at org.springframework.aop.framework.JdkDynamicAopProxy.invoke(JdkDynamicAopProxy.java:198),
	at com.sun.proxy.$Proxy127.lookup(Unknown Source),
	at com.rsa.authmgr.internal.admin.tokenmgt.impl.TokenAdministrationImpl.a(TokenAdministrationImpl.java:1581),
	at com.rsa.authmgr.internal.admin.tokenmgt.impl.TokenAdministrationImpl.lookupPrincipal(TokenAdministrationImpl.java:1738),
	at com.rsa.authmgr.admin.tokenmgt.ListTokensByPrincipalCommand$Executive.execute(ListTokensByPrincipalCommand.java:2),
	at com.rsa.authmgr.admin.tokenmgt.ListTokensByPrincipalCommand.performExecute(ListTokensByPrincipalCommand.java:120),
	at com.rsa.command.LocalTarget.executeCommand(LocalTarget.java:119),
	at com.rsa.ims.command.LocalTransactionalCommandTarget.access$0(LocalTransactionalCommandTarget.java:1),
	at com.rsa.ims.command.LocalTransactionalCommandTarget$2.doInTransaction(LocalTransactionalCommandTarget.java:268),
	at com.rsa.ims.command.LocalTransactionalCommandTarget$2.doInTransaction(LocalTransactionalCommandTarget.java:1),
        at org.springframework.transaction.support.TransactionTemplate.execute(TransactionTemplate.java:131),
        at com.rsa.ims.command.LocalTransactionalCommandTarget.executeCommand(LocalTransactionalCommandTarget
Cause
Resolution
- Login to the primary's Operations Console using the Operations Console Administrator username and password.
- Navigate to Deployment Configuration > Identity Sources > Manage Existing.
- When prompted, enter the super admin username and password.
- Click on the affected identity source and select Edit.
- On the Map tab, make sure that both the Users Search Filter and the User Groups Search Filter are correct for your deployment.
- Click Save.



